Railway Breach Exposed AI Keys, $740,000 in Stolen Spend
By Christine James, Editor · November 10, 2026
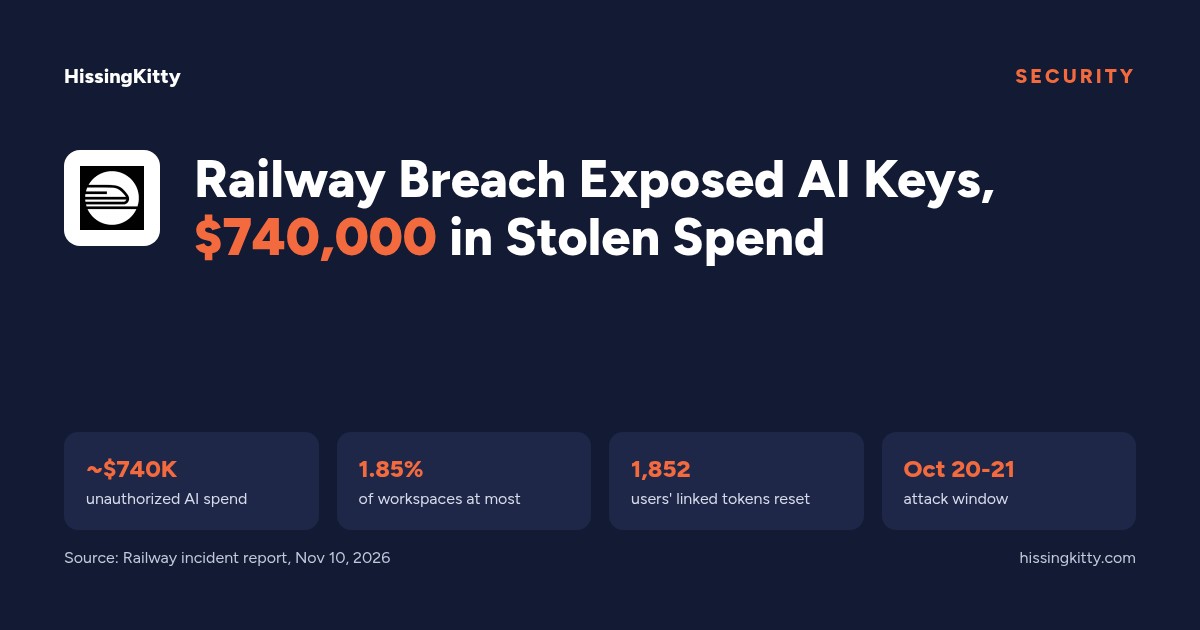
Railway, the app hosting platform, says an attacker broke out of its build system in October and decrypted customer environment variables, the settings where apps keep passwords and API keys. The attacker went after AI provider keys first. Railway estimates about $740,000 was spent on those stolen keys before they were shut off.
That number is the lesson. Stolen AI keys now turn into real money within hours, and they sit inside hosting platforms that most finance teams never review. Railway's full incident report, published Nov 10, 2026, is one of the most detailed any hosting company has shared.
Key facts
- The attack ran from Oct 20 to Oct 21, 2026, per Railway's incident report.
- At most 1.85% of Railway workspaces, about 100,000, could have had environment variables decrypted. Railway calls this an upper bound.
- AI provider keys were the main target, according to Railway's review of the attacker's queries.
- Linked tokens for 1,852 users, including bring-your-own AI keys and GitHub tokens, were decrypted and reset.
- Unauthorized spend on stolen keys was estimated at about $740,000. Railway is seeking refunds and says it will cover the rest.
- Railway found no sign that customer databases or code were accessed.
What Happened at Railway?
Railway builds customer apps on shared machines, with each build walled off from the others. The attacker found a way out of that wall, picked up a build credential and used it to reach internal systems. From there it chained a misconfigured sign-in exchange to a longer-lived credential stored on an orchestration machine, which could decrypt customer variables. Here is the timeline from Railway's report, all times UTC:
| 2026 | What happened |
|---|---|
| Oct 20, 06:50 | The attacker starts probing Railway's shared build machines, where several customers' builds ran side by side. |
| Oct 20, 13:58 | Railway engineers spot the unauthorized access. |
| Oct 20, 17:03 | Railway halts builds for the first time, then restores them after believing the path is closed. |
| Oct 21, 04:07 to 05:21 | Using a misconfigured login exchange and a credential left on an internal machine, the attacker pulls and decrypts a subset of customer variables. |
| Oct 21, 07:22 | Builds halted again. Cloud credentials disabled, decryption service shut off. |
| Oct 21, 09:25 | Railway's last record of attacker access. It notifies AI providers with lists of exposed keys. |
| Oct 22, 22:49 | Builds restored for all plans on new single-tenant build machines. |
| Nov 10 | Railway publishes its full incident report. |
Railway first shared what it knew in a preliminary report while recovery was still underway, then followed with the full write-up.
What Was Exposed, and What Wasn't?
Railway says the attacker searched variable names for AI provider keys and decrypted keys for a subset of the matching environments. One more search matched cloud, database and payment credentials. Railway also says the attacker favored customers with many variables.
On the other side, Railway found no sign that customer databases were accessed or that customer code was downloaded. Running apps stayed online. The pain came from paused builds: teams that rotated a key could not redeploy with the new one until builds returned on Oct 22, and Railway says some customers had downtime because of that. New signups were paused too.
Railway believes the stolen AI keys were passed on for distillation, using someone else's paid access to copy a model's answers. That is Railway's assessment, not a confirmed finding.
Who Pays for the $740,000?
Railway says the unauthorized spend on stolen keys was estimated to reach about $740,000. It is working with AI providers to refund customers and says it will cover the cost from its own balances where a provider won't. Railway hasn't said how much has been refunded so far, so treat the $740,000 as an estimate of exposure, not a final bill.
For buyers, this is the new shape of a breach bill. A stolen password costs you a reset. A stolen AI key with no spend cap costs you whatever the attacker can run before someone notices.
What Should Teams Do Now?
- Rotate keys stored on Railway. If you got an email from Railway, follow its remediation guide. If you didn't, rotating AI, cloud and payment keys is still cheap insurance.
- Set spend caps at every AI provider. A hard monthly limit turns a stolen key from an open tab into a capped loss.
- One key per app. Separate keys mean you can revoke one app's access without taking down the rest.
- Check the AI bills, not just the hosting bill. Unusual usage at your AI provider is often the first sign a key is out.
- Add hosting to procurement. Ask how builds are isolated and how secrets are encrypted. Our software procurement guide covers the questions.
Should You Leave Railway?
Not on this alone. Railway found the attacker, cut access, reset every session and token, moved builds to single-tenant machines and published a timeline with exact times. That is how a vendor should handle it. Every hosting platform stores your secrets somewhere, so moving does not remove the risk; your own key hygiene does more.
If you were already comparing hosts, Railway's alternative listing shows what buyers say, and the Heroku company page lists other options with real prices and reviews. The Build vs. Buy calculator helps if you're weighing running it yourself.
Where This Does Not Apply
If you don't host on Railway and don't store AI keys in any hosting platform, this incident doesn't touch you directly. Teams running small apps with spend caps already in place have little to do beyond a routine key rotation.
We log confirmed incidents like this one in the Software Security Incidents 2026 tracker.
Sources: Railway incident report, Railway preliminary report. This story will be updated if Railway shares more, such as refund totals.
Built Something Like This?
List it free, or tell other teams what you pay today.