Java4Shell Is Patched. Now Ask Your Vendors
By Christine James, Editor · November 17, 2026
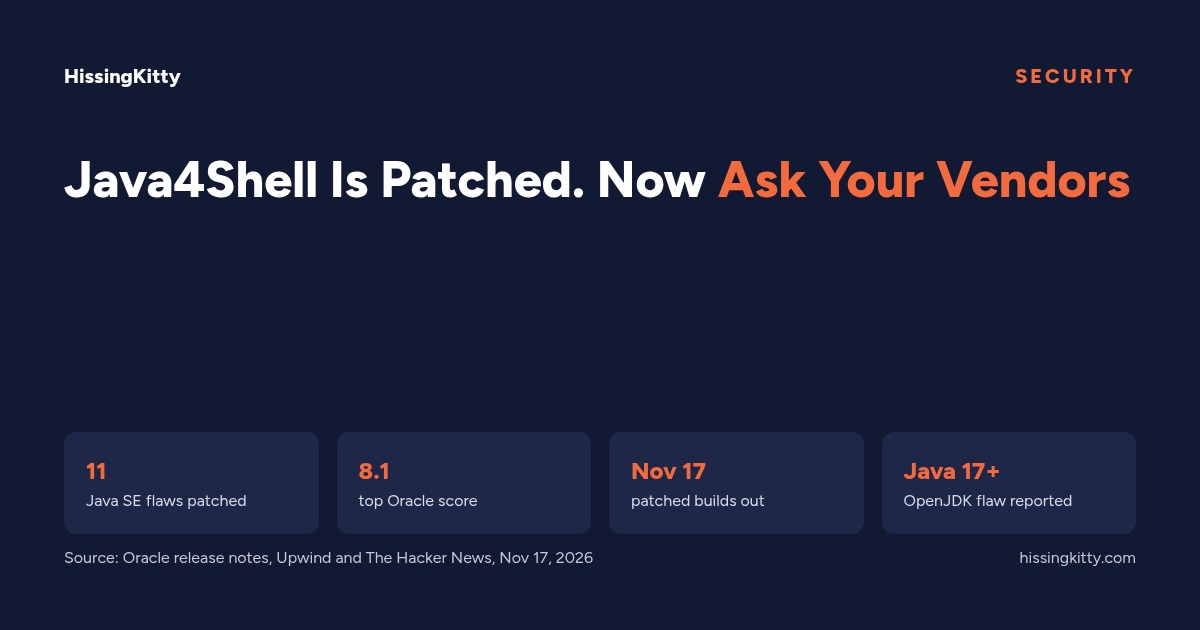
Security teams spent Tuesday patching Java. Oracle shipped updates on November 17, 2026 for 11 Java SE flaws, on the same day a separate OpenJDK bug, nicknamed Java4Shell, leaked before its fix was public. Java runs underneath a large share of business software, so most companies are affected through their vendors as well as their own servers.
The useful step for a software buyer is short: ask each vendor that runs Java whether they have patched, and by when. This piece explains what is known, what is not, and the exact questions to send.
Key facts
- Oracle released Java SE updates on November 17, 2026, fixing 11 vulnerabilities that can be exploited remotely without a login, with a top CVSS 3.1 score of 8.1.
- A separate OpenJDK flaw, CVE-2026-114938 or "Java4Shell," leaked before its fix and is reported at 9.2 under CVSS 4.0.
- Upwind reproduced the bug: a malformed Base64 string makes Java's decoder write 62 bytes past the end of its output, on x86-64 CPUs with AVX-512 VBMI.
- Upwind found Java 17.0.6 and later, 21 and 25 affected, and Java 8 and 11 not. Code execution was not proven in its tests.
- Oracle's fixed builds end in .1, for example 17.0.21.1 and 21.0.13.1. Fixes from Temurin, Corretto and Zulu were still pending when Upwind published.
What Oracle Patched on November 17
Oracle's November update covers Java SE 8, 11, 17, 21, 25 and 27. The Hacker News reported that all 11 flaws can be exploited remotely without authentication, with a top score of 8.1, and that Oracle had not named the affected parts ahead of release. The Java 8u513 release notes confirm the November 17 release and say the next scheduled patch is January 19, 2027.
What Java4Shell Is, and What Is Still Unknown
Upwind reproduced the bug on real hardware. A malformed Base64 string makes Java's hardware-accelerated decoder write 62 bytes past the end of its output. Only x86-64 CPUs with AVX-512 VBMI run the affected code, so ARM servers and older Intel chips are not exposed.
The flaw can be reached before login: Upwind says standard Basic auth in Spring Security, Tomcat and Jetty pass attacker input to the decoder before checking anything. It also says reaching the bug is not the same as damage, and that code execution was not proven in its tests. The CVE record was still reserved without a public description at the time of writing.
- Known: the overflow is real, it is reachable before login, and Oracle's .1 builds are out.
- Not known yet: whether it allows running code, and when every OpenJDK distribution ships a fix.
Why Software Buyers Should Care
Most teams don't run Java themselves. Their CRM, ERP, help desk or file-sharing vendor does. A vendor that runs an unpatched server on affected hardware is the exposure, and buyers usually learn about it only if something goes wrong. Past events are on our 2026 software breach tracker. We will add a company there only if it confirms it was affected; a patch on its own is not a breach.
Five Questions to Send Your Vendors
- Do any of the systems that hold our data run Java 17, 21, 25 or 27?
- Have you installed the November 17, 2026 Java updates, or a fixed OpenJDK build? If not, by what date?
- Until then, have you turned off the Base64 intrinsic (
-XX:-UseBASE64Intrinsics), which Upwind found stopped the overflow? - Have you seen any sign that the flaw was used against your systems?
- Will you tell us in writing if that changes?
A clear, dated answer is a good sign. A vague one is worth noting before the next renewal, alongside price and support.
Where This Does Not Apply
If a vendor runs on ARM servers, on older Intel chips, or on Java 8 or 11 only, Upwind's findings say the Java4Shell code path is not reached, though Oracle's other November fixes still apply. Tools that don't use Java at all are outside this issue.
Does This Apply to You?
- You run Java services yourself: patch to the .1 builds today.
- You rely on vendors for core systems: send the five questions this week.
- You use Oracle products that bundle Java: check Oracle's patch documents for each one.
For a full list of affected and fixed builds, see Aikido's version table. If a vendor's answer changes how you feel about them, say so in a review.
Oracle on HissingKitty
No bills yet
What teams pay
No ratings yet
Ratings
10
Alternatives listed
Built Something Like This?
List it free, or tell other teams what you pay today.