Notion AI Chats Exposed in Fireworks AI Breach: What Teams Should Do
By Christine James, Editor · November 10, 2026
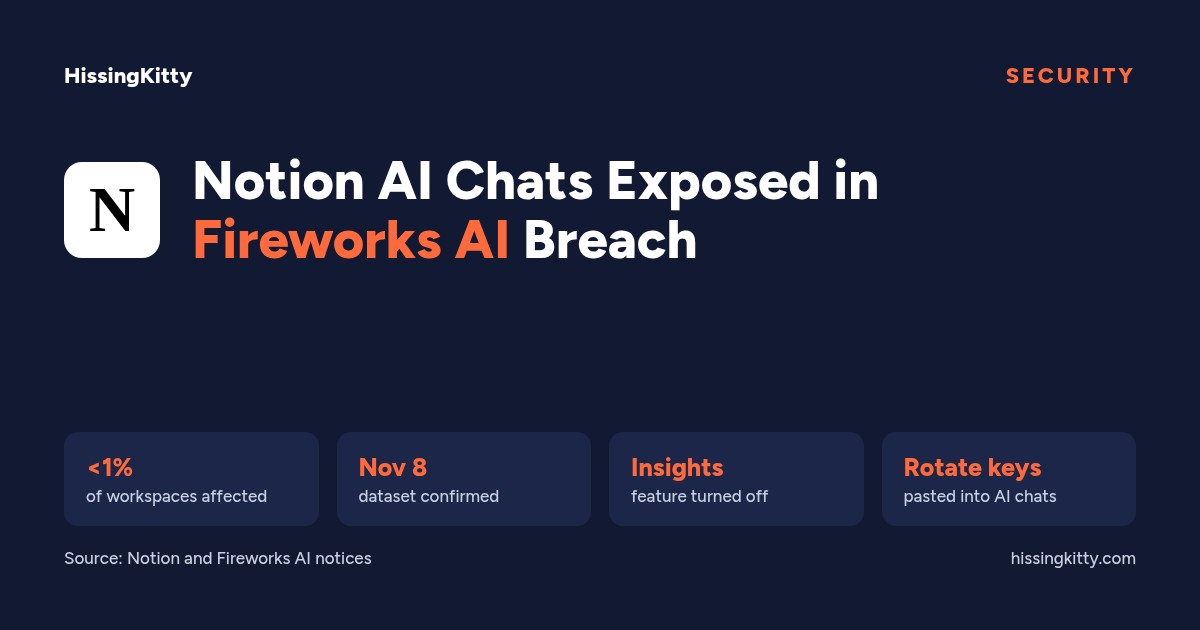
Notion says a breach at one of its AI vendors, Fireworks AI, exposed Notion AI chat transcripts from fewer than 1% of its workspaces. Notion's own systems were not breached. The data sat with a supplier most Notion customers had never heard of, which is the part worth paying attention to.
Notion has contacted affected workspace owners and posted a public notice. If you haven't heard from Notion, it says your workspace is not affected and no action is needed right now.
Key facts
- Fewer than 1% of Notion workspaces may have been affected, according to Notion.
- The exposed data is Notion AI chat transcripts used for Notion's Insights feature.
- Notion calls the chats "unattributable": they carried no user or workspace label and no tool call results, such as page content.
- Notion has turned off Insights and no longer serves open-weight models through Fireworks.
- Notion advises treating the data as exposed and rotating any passwords or API keys pasted into Notion AI.
What Happened?
Fireworks AI runs open AI models for other companies on its own servers. Notion used it for two jobs: classifying chats for Insights, a feature that shows customers how their team uses Notion AI, and serving open-weight models inside Notion. Here is the timeline from Notion's advisory and Fireworks' bulletin:
| 2026 | What happened |
|---|---|
| Oct 9 | Fireworks AI publishes its first security bulletin. At that point only secrets stored with Fireworks were known to be accessed. |
| Oct 23 to 24 | Per Fireworks, a cloud provider hosting its R&D machines has an incident, and the attacker uses it to reach Fireworks development machines. |
| Nov 2 | Fireworks tells Notion a small set of data was accessed. Notion says it was synthetic test data. |
| Nov 3 | Notion disconnects from Fireworks, deletes its data there and stops sending traffic. |
| Nov 6 | Fireworks tells Notion attackers may have accessed customer data. |
| Nov 8 | Fireworks confirms the new dataset. It includes Notion AI chat transcripts used for the Insights feature. |
Fireworks says it notified law enforcement and brought in Palo Alto Networks Unit 42 for forensics. It links the activity to a financially motivated group that resells stolen access to AI models, a practice Google's threat team calls "LLMJacking". Fireworks also reports impacts to account and billing information and, for a limited set of accounts, to secrets, datasets and incomplete models.
What Was Exposed, and What Wasn't?
Notion says the dataset held chat transcripts only. No pages, files or other workspace data were affected, and the transcripts did not include tool call results, the page content or outside data Notion AI pulls in to answer.
"Unattributable" means the chats weren't labeled with a person or workspace. That limits how easily anyone can tie a chat back to a company. It does not make the words in the chat harmless. People paste contract terms, customer names, financials and sometimes credentials into AI chats, and any of that would still be readable. Notion says the same thing: treat the data as exposed.
Affected workspace owners can review the data from the sidebar under the help menu, then "Security incident review." Enterprise owners get a CSV; other plans get a link to share with affected members.
Why It Matters to Software Buyers
Most teams review a vendor's security once, at purchase. AI features quietly add new suppliers behind that vendor: model hosts, classification services, evaluation tools. Each one holds a copy of what your team types. This incident is a clear case of that chain, and it will not be the last.
That isn't a reason to stop using AI features. It is a reason to know where your data goes. We now log confirmed incidents like this one in the Software Security Incidents 2026 tracker, alongside our layoffs tracker.
What Should Teams Do Now?
- Rotate secrets. If anyone pasted passwords, API keys or tokens into Notion AI, rotate them today, whether or not you got an email.
- Check the review page. Workspace owners who were notified should pull the affected data and look for sensitive content.
- Ask for the sub-processor list. Every AI feature you pay for should come with a list of the companies that process your data. Ask for it before your next software renewal.
- Set a rule for AI chats. No credentials, ever. Treat an AI chat like an email to an outside party.
- Add it to procurement. Our software procurement guide covers the questions to ask about third parties.
Should You Keep Using Notion?
For most teams, yes. Notion found the exposure, cut the vendor off, turned off the affected feature and published what it knew, with dates. That is how a vendor should handle a supplier breach. If your team keeps sensitive work in Notion AI, the steps above matter more than switching.
If you were already weighing a move, see the Notion company page for real buyer reviews, prices and alternatives, or run a spend audit to see what your stack costs.
Sources: Notion help center notice, Notion security advisory, Fireworks AI security bulletin. This story will be updated if either company shares more.
Notion on HissingKitty
$264 /yr
Median of 6 teams
3.0
1 rating
4
Alternatives listed
Built Something Like This?
List it free, or tell other teams what you pay today.